
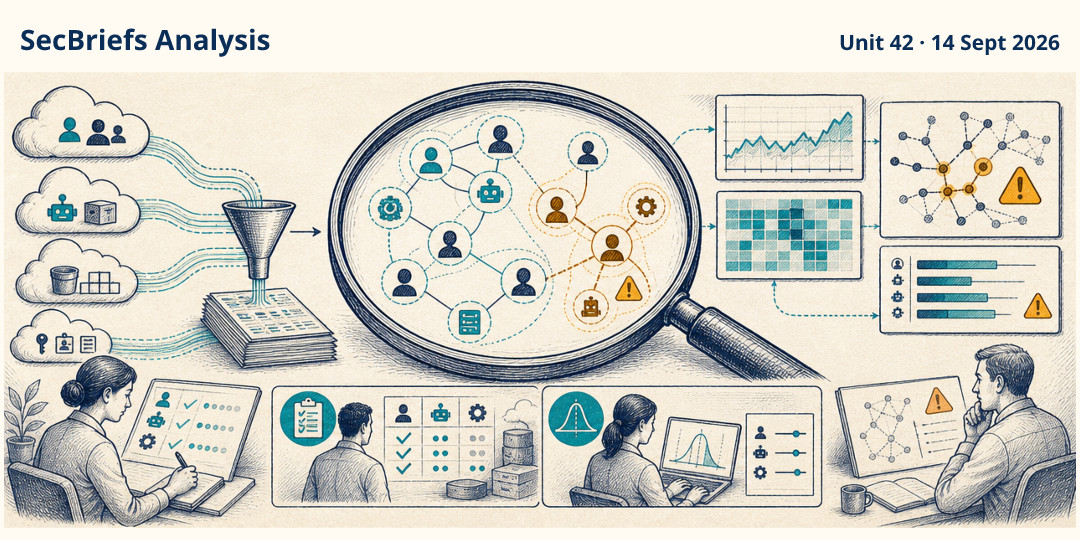
Behavioral clustering offers a way to map cloud identities from audit logs
DECISION SNAPSHOT
KNOWThe signal in one glance
VerdictKNOW
ThemeCloud Security Research
VerificationVerified
SourceUnit 42
Source dateSep 14, 2026
Read time2 min
What you need to know
- Unit 42 describes a behavioral clustering model that maps cloud identity roles from audit logs and supports continuous threat detection using standard SQL queries.
- Cloud identity misuse can be difficult to see when organizations have many roles, service accounts, and changing workloads.
- Action: Inventory which cloud identity, role, and audit events are available, retained, and searchable across environments.