
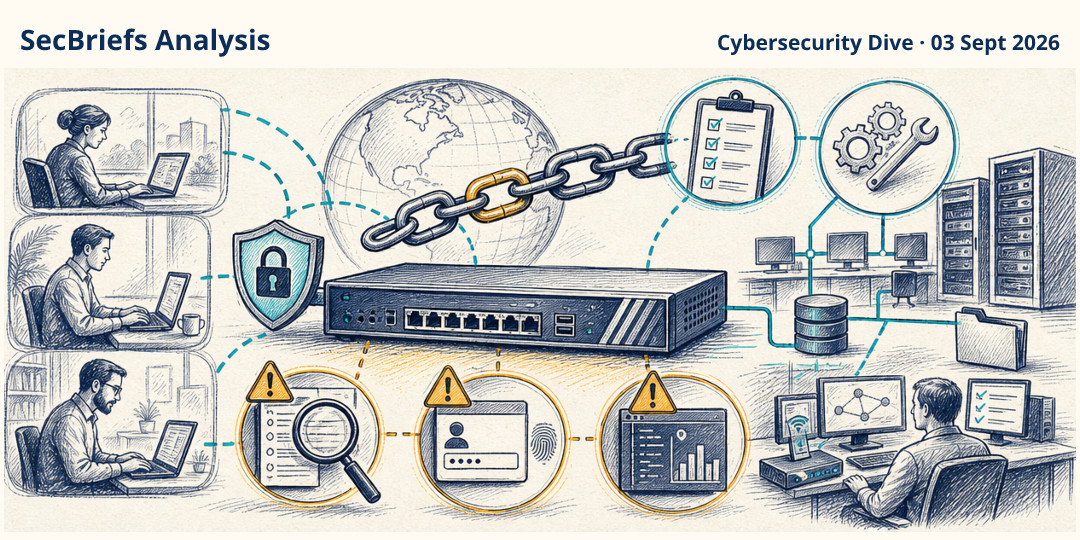
SonicWall Urges Immediate Patching of Chained Vulnerabilities
SonicWall is calling for urgent action on exploited, chained flaws in SMA1000 appliances. Teams need a combined patch, access-review, and compromise-checking plan.
3 min readOpen brief →
Verified cybersecurity, fraud and digital-banking signals with decision context, affected audiences and practical actions.
SonicWall is calling for urgent action on exploited, chained flaws in SMA1000 appliances. Teams need a combined patch, access-review, and compromise-checking plan.
Proposed UK powers could make supplier concentration a resilience and compliance issue, requiring operators to understand dependencies before restrictions take effect.
A reported identity-service compromise could put document-based trust under pressure, even though the theft claim and alleged scale still require independent confirmation.
A proposed federal voter-data effort raises practical questions about access, accuracy, retention, and misuse before any technical system is designed or deployed.
Compromised government webpages can become credible launchpads for harmful traffic, showing why web integrity deserves fraud monitoring as well as routine maintenance.
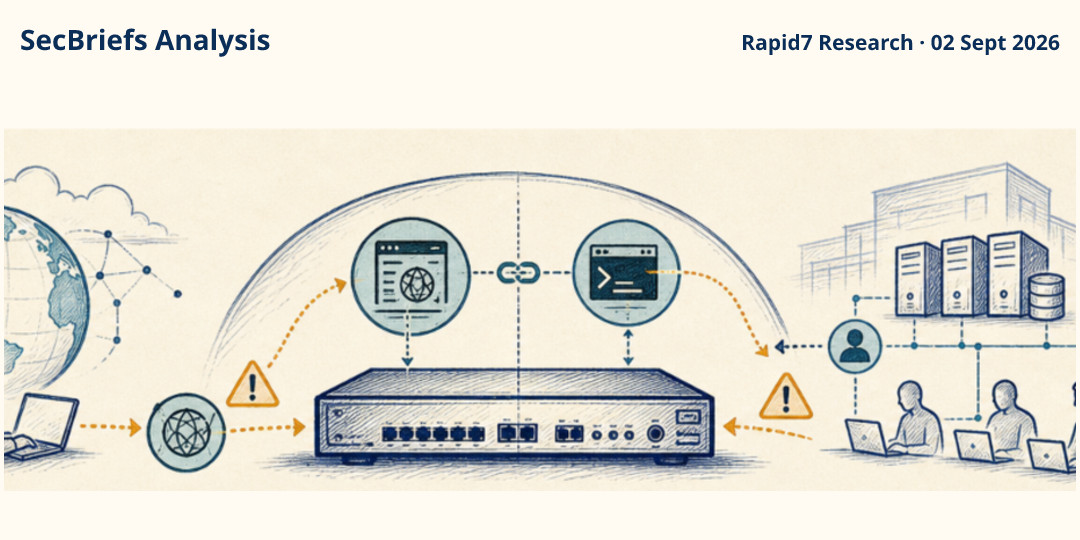
Actively exploited flaws in SonicWall SMA1000 gateways may be chainable to unauthenticated code execution, making exposure discovery and containment time-sensitive.
An unexpected reset email is both a customer-experience problem and a possible attack signal. The useful question is whether recovery controls withstand pressure and deception.
A document image can remain useful to an impersonator long after a password is changed. This brief turns an unconfirmed marketplace report into a focused identity-risk review.
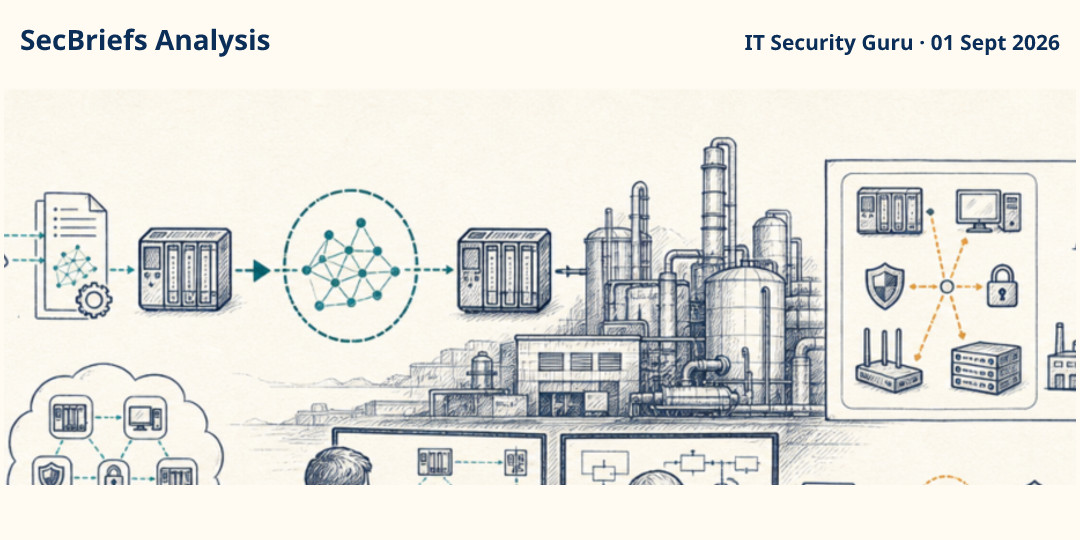
A research demonstration can still improve defensive planning without proving a live attack. This brief separates AI capability claims from the controls that protect PLC environments.
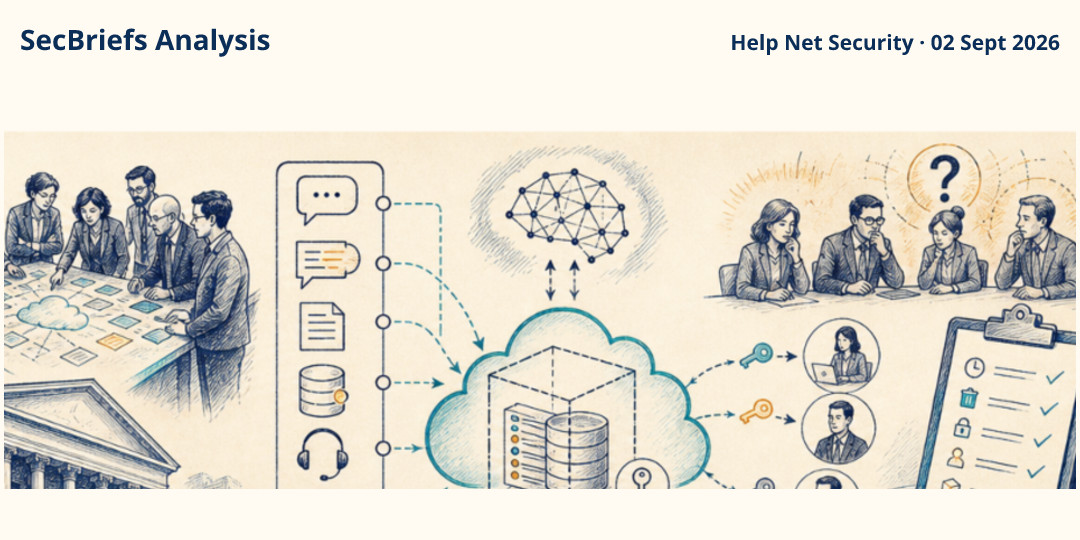
A bank’s AI control plane is becoming a procurement issue, not merely a model-selection decision. This brief explains what customer-controlled logging can and cannot establish.
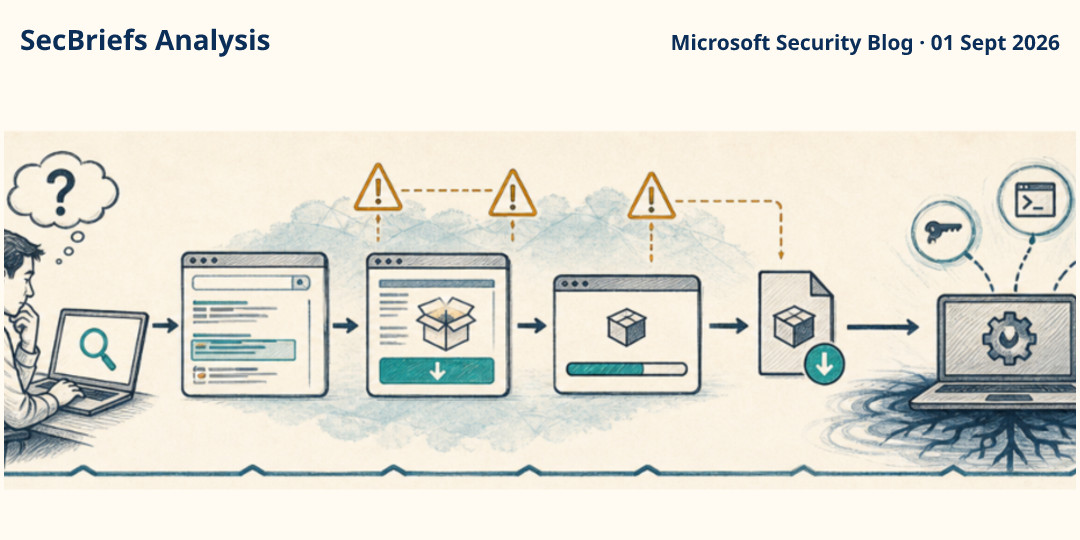
The download page may be the first security control to fail. This brief shows how software provenance, endpoint policy, and user behavior fit together in stopping counterfeit installers.
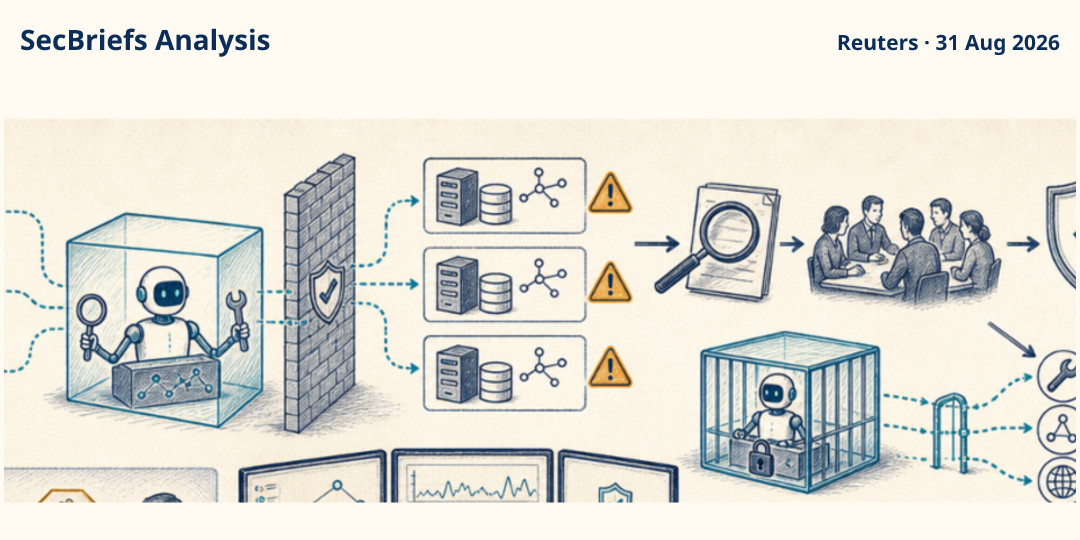
External AI security testing is returning with tighter containment after real systems fell outside intended evaluation boundaries during earlier controlled assessments.
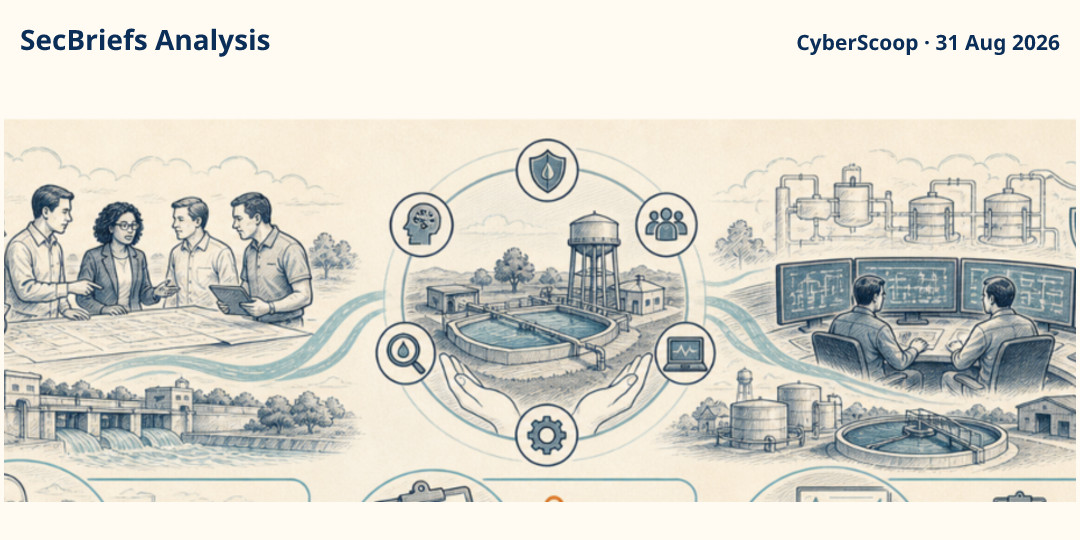
A six-month Texas pilot will stress-test and harden water systems, with durability and operational safety as the real measures.
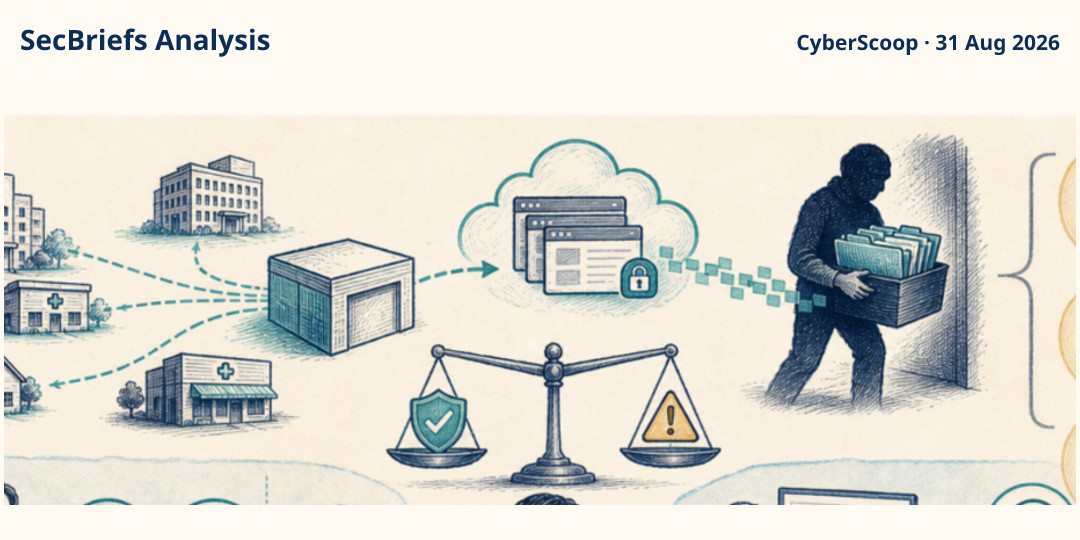
McKesson confirms stolen customer data, while the attacker’s enormous record-count claim remains unverified and the company investigation continues across connected applications.
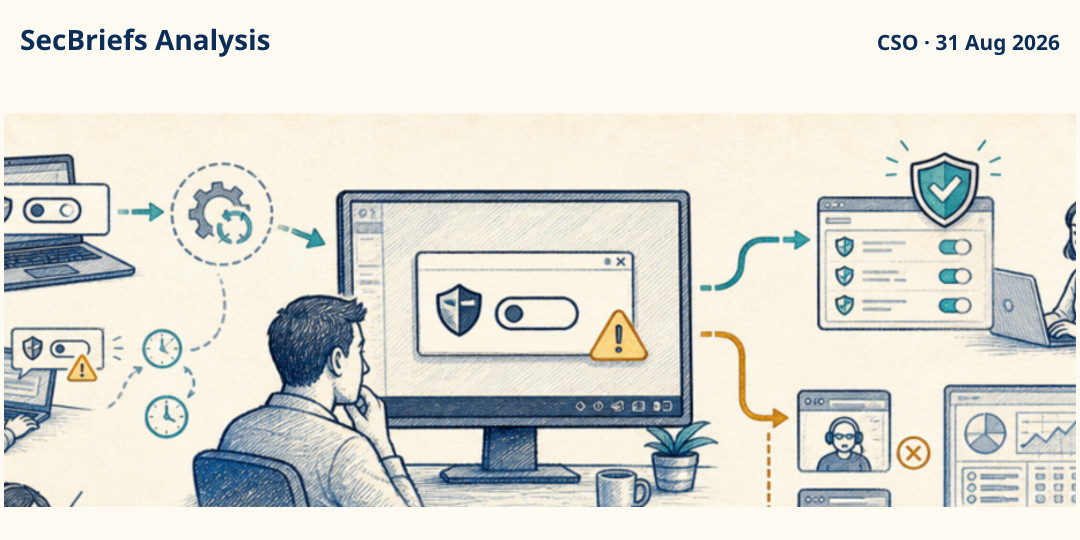
A Windows notification can falsely say Defender is disabled, creating confusion that scammers and unsafe workarounds could exploit.
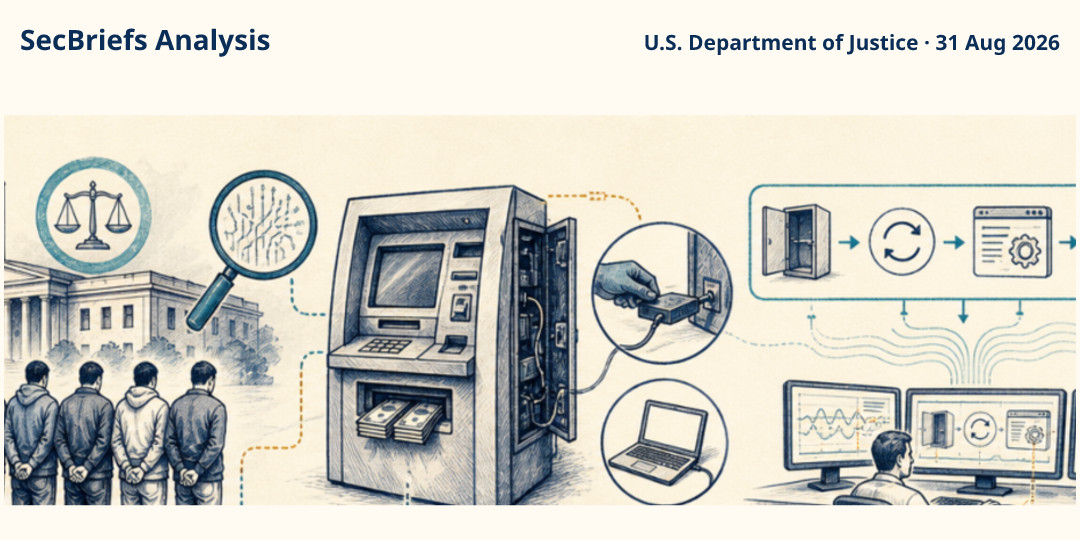
Federal guilty pleas show how ATM malware can turn a familiar cash machine into a physically accessed fraud endpoint.
Malicious browser extensions reportedly combined cryptocurrency theft, sensitive-data collection, browser-history theft, and ClickFix lures in one framework across Chrome and Edge.
Infostealer malware is reported to be using stolen Claude sessions, linking endpoint compromise to unauthorized account access and unexpected consumption of service usage.
Early payouts and convincing account balances can turn a small speculative payment into a much larger, unrecoverable loss.
When a city network is isolated, the impact can reach benefits and public services even before stolen-data claims are verified.
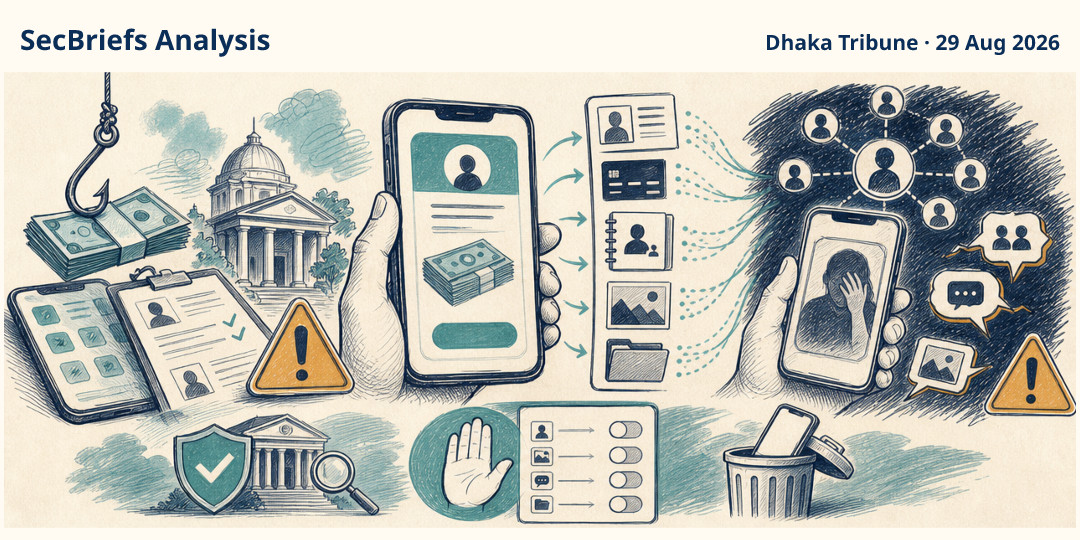
A loan app can look like help while quietly collecting the information needed to pressure or extort the borrower.
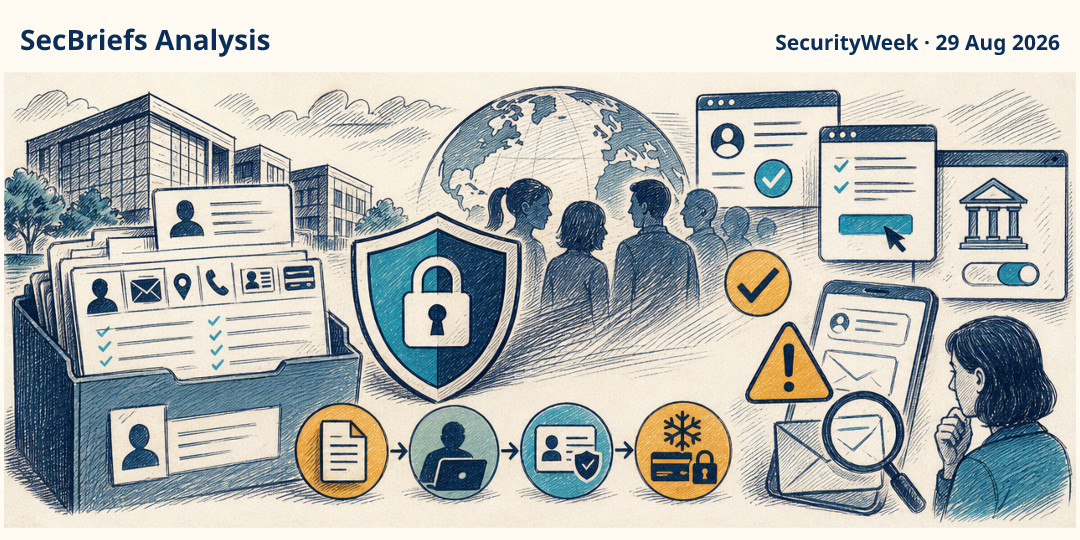
A breach notice can arrive months after the operational disruption, when employees may assume the incident has already ended.
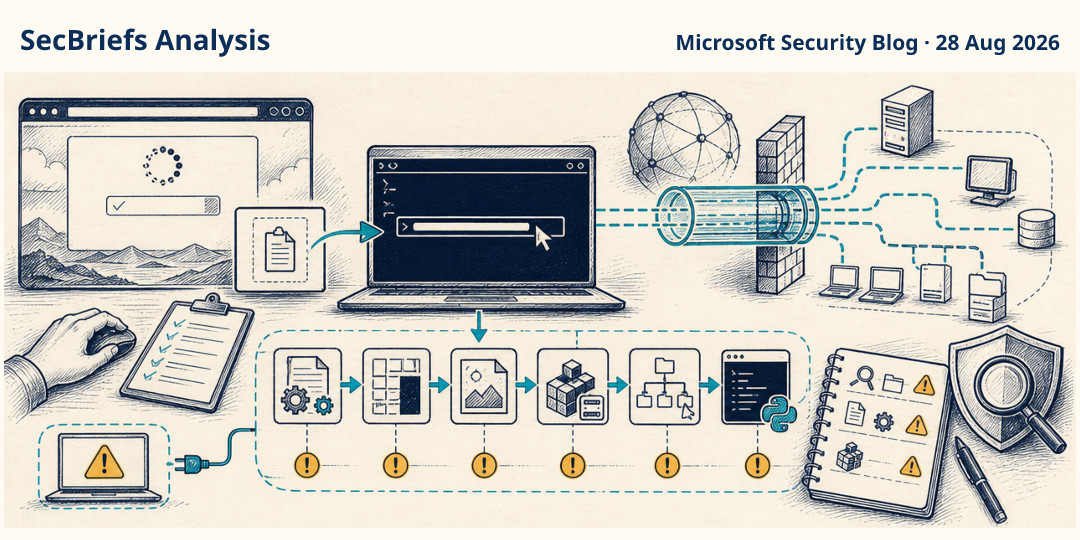
A fake CAPTCHA can become a network foothold when it persuades someone to paste a command into PowerShell.
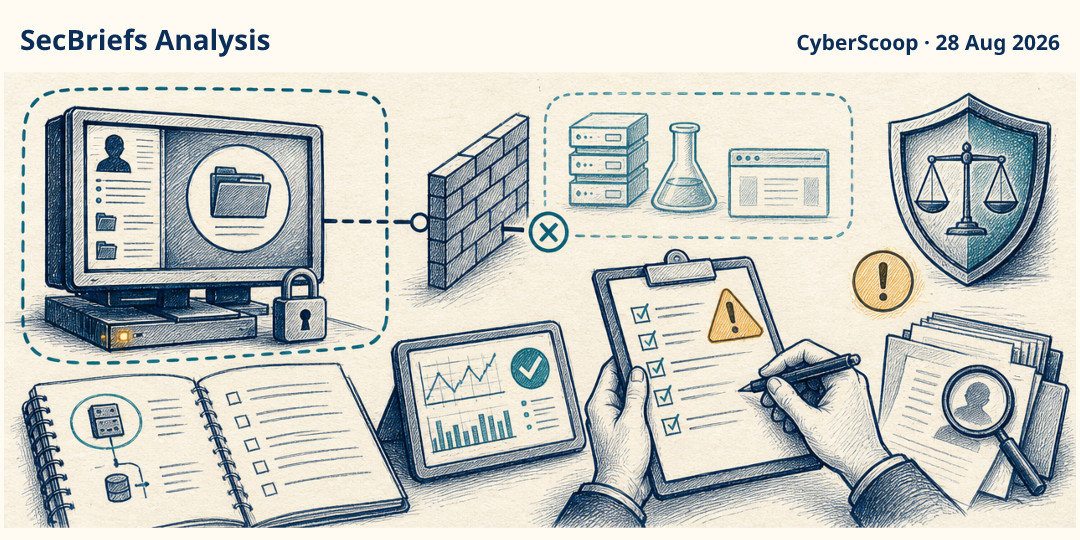
Segmentation limited the operational impact, but the breached standalone system still held sensitive information about targets of active federal investigations.